Operator-grade counterintelligence training, built around your mission.
We don’t run canned courses. Every program is shaped to the people in the room, the threats they face, and the work they have to do when they walk out the door.
OUR PHILOSOPHY
T2P: Tailored Theory to Practice
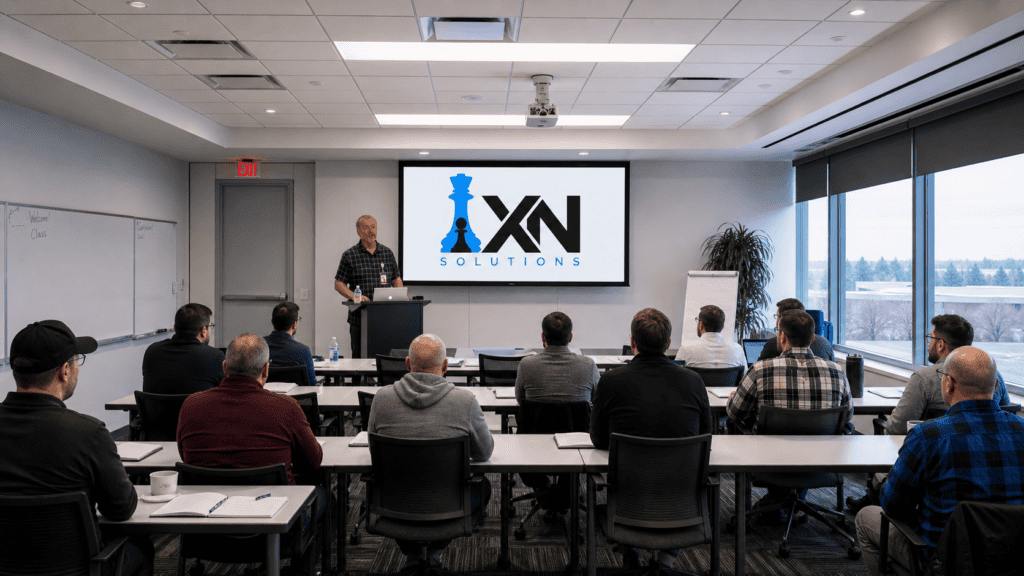
Most training falls down in the same place. The doctrine is solid, the examples are old, and nothing in the room maps to what your team will see on Monday. T2P fixes that. We start with your mission and end with your people running scenarios that mirror what they actually face.
1
2
3
4
Mission Discovery
We sit down with your leadership and operators before we write a single slide. What’s the threat picture? What’s working? Where are the gaps you can’t close with the team you have?
Curriculum Build
Doctrine, tradecraft, and case studies get tailored to your operating environment. No filler blocks. No recycled decks from last year’s audience.
Practical Application
Theory only sticks when people use it. We close every block with scenario work, role plays, and table-top exercises drawn from real cases.
Reinforcement
Training day ends but the work doesn’t. We hand off job aids, after-action notes, and follow-up touchpoints so skills carry into the field.
Why T2P Works
Our instructors have done the work. They’ve run sources, sat in interviews, built CI cases, and managed insider threat investigations. They know where doctrine breaks down and how to teach around it.
Every cohort leaves with two things: tradecraft they can defend in front of a senior officer, and the muscle memory to apply it under pressure.
FOCUS AREAS
Where We Have Operational Depth
Our instructor cadre has spent careers in these disciplines. We don’t teach what we read about. We teach what we did.
Counterintelligence
Threat awareness, defensive CI, investigations, and analysis grounded in real casework.
HUMINT
Spotting, assessing, developing, and handling sources. Operational planning and reporting.
Surveillance
Detection, route planning, surveillance teamwork, and operational security in hostile environments.
Elicitation
Conversational collection techniques, recognition of elicitation, and counter-elicitation.
Investigations
Case management, interviews, evidence handling, and reporting to a standard that holds up.
CI Operations
Operational planning, target packages, effects-based ops, and full-cycle case execution.
Insider Threat
Indicators, program build-out, investigations, and the cultural piece most programs get wrong.
Cyber CI
Where cyber tradecraft meets CI. Hunting adversary tradecraft, attribution, and integrated response.
TEACHING IN ACTION
How a T2P Course Runs
Three building blocks reinforce learning and let us evaluate how well it sticks.
Tailored Theory and Doctrine Review
We open with the doctrine that applies to your mission, mapped to your environment, not somebody else’s.
Instructor “Best Practice” Demonstration
Instructors demonstrate performance to standard, use real cases references, and answer questions.
Small Group Scenario Employment
Teams run the scenario themselves under time and information pressure, then debrief against the standard.
WHAT CLIENTS SAY
From the People We’ve Trained
Names and units redacted on request. Quotes provided with permission.
“The team didn’t just lecture us. They walked through actual cases, broke down what worked and what didn’t, then put us through scenarios that mapped to what we’d see the next week. Best CI training my unit has had in years.“
Senior CI Officer, DoD Component
“What set this apart was the prep. They reviewed our mission set, talked to our leadership, and built something specific to us. We weren’t sitting through a generic course pulled off a shelf.“
Program Manager, Federal Agency
“Our analysts came back with skills they were using inside 48 hours. The instructors have been there. You can tell the difference inside the first hour of class.“
Branch Chief, Intelligence Community
“I’ve put three cohorts through their elicitation block. Every group has come out sharper, more confident in source meetings, and better at recognizing when someone is working them.“
HUMINT Operations Lead, Interagency Task Force
Bring T2P to Your Team.
Tell us about your mission and the gap you’re trying to close. We’ll come back with a curriculum built for the people in your room.
Last Updated: 2 May 2026